OpenCode Breach Leaks API Keys, Drains AI Accounts Overnight
Does the Console breach expose dangerous gaps in AI credential security or does the swift response prove the industry's resilience?
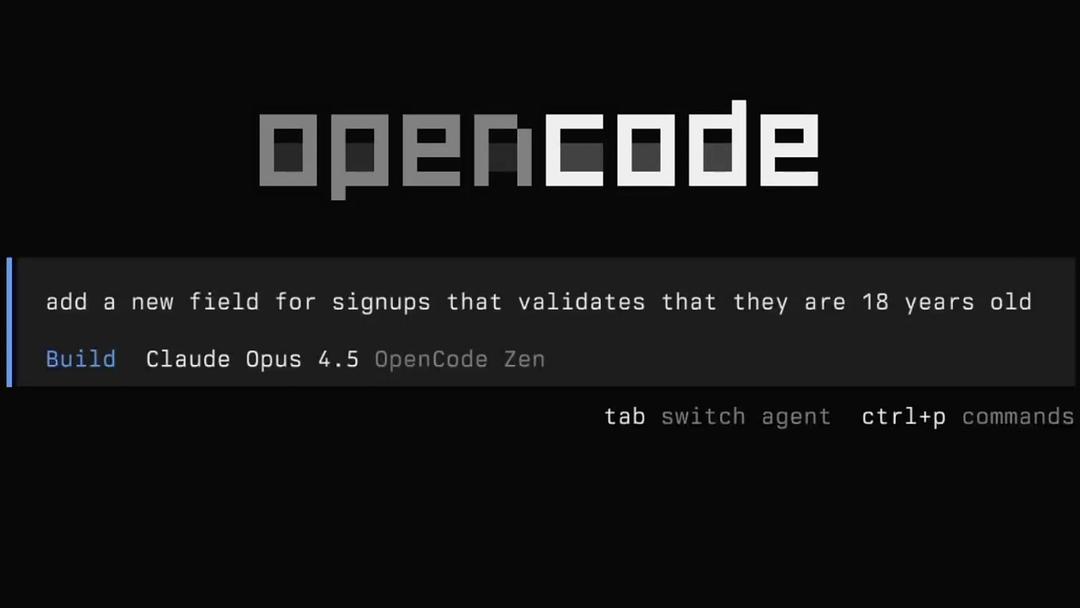
Above: OpenCode home screen. Image credit: OpenCode
The Facts
- OpenCode, an open-source AI coding agent, said Saturday that an intruder accessed an older system overnight, affecting 1.4% of OpenCode Console users, where some developers store API keys. The company said the breach was “related to a large-scale distillation attack." It emailed those affected and said it was working with Anthropic, OpenAI and Google.
- Co-founder Dax Raad wrote on X on Sunday that attackers had been "non stop trying to attack our systems for the past 48 hours," adding that one side effect was that the company's systems were being "hardened." OpenCode said the incident remained ongoing.
- Anthropic and Google blocked API keys they believed were exposed, and OpenAI said it worked with OpenCode to restore access and refund credits used during the attack. OpenCode said it was processing refunds for unauthorized charges.


Sources Split
LEFT
CENTER
RIGHT
+1
+1
+3

ESTAB
CRIT
CENTER
PRO
ESTAB
The Spin
Narrative A
This breach exposed vulnerabilities in Console infrastructure, putting stored AI provider API keys at risk. The incident raises urgent questions about credential protection, incident response and financial safeguards across AI development platforms, as that gap is where the next breach starts.

Narrative B
OpenAI and OpenCode worked closely to help affected users who rely on OpenAI API services get back in business quickly and to refund credits for eligible usage consumed during the attack. This shows that AI firms are committed to helping developers recover and stay resilient.



© 2026 Improve the News Foundation. All rights reserved.Version 7.18.2
© 2026 Improve the News Foundation.
All rights reserved.
Version 7.18.2